Penetration Testing (VAPT)
01Authorised, scoped testing of your networks, applications and infrastructure, combining automated discovery with manual exploitation and a full retest cycle.
- Manual Testing
- Scoped
- Retested
Asematic delivers cyber security services in India for teams that need findings fixed rather than filed. Manual penetration testing against your real environment, compliance readiness for ISO 27001, SOC 2 and the DPDP Act, and every finding retested before the engagement closes.
Engagement standard
How every engagement is run, agreed in writing before any testing begins.
A scan is run, a report is filed, a certificate is framed. None of it is the same as being harder to breach, and the distance between the two is where most security budgets quietly go.
What it costs you
A two-hundred-page report nobody has time to act on
Severity is scored against what an attacker could realistically reach and what it would cost you. The first five items are the ones worth a developer sprint, not the ones the tool listed first.
What it costs you
A scanner export rebadged as a penetration test
Scanners find known signatures. Business logic flaws, broken access control, privilege escalation and chained exploits are found by a person who understands what your application is trying to do.
What it costs you
Critical bugs first mentioned in the final readout
If we find something that puts customer data at immediate risk, you hear about it that day with a mitigation, not three weeks later when the report is formatted.
What it costs you
Fixes marked done with nobody checking
A fix that does not actually fix the issue is worse than a known gap, because it is now recorded as closed. We retest each one, and check whether the change opened anything adjacent.
What it costs you
A compliance certificate with the same gaps underneath
Certification follows real controls. We build the controls, generate the evidence trail they produce, and prepare you for the auditor — rather than assembling documentation around gaps.
What it costs you
No plan for the morning the breach is real
Who is called, what is isolated, what is preserved for forensics, who notifies regulators and customers, and within what window — walked through with your team before you need it.
A pre-launch application test and a certification programme are different problems. They are run with the same discipline: written authorisation, manual verification, and findings closed rather than listed.
Authorised, scoped testing of your networks, applications and infrastructure, combining automated discovery with manual exploitation and a full retest cycle.
Testing against the OWASP Top 10 and beyond — access control, authentication, injection, business logic and API authorisation flaws that scanners routinely miss.
AWS, Azure and GCP configuration reviewed against CIS benchmarks: IAM policy, network exposure, storage permissions, secrets handling and logging coverage.
iOS and Android testing covering local storage, certificate pinning, reverse engineering resistance, and the backend APIs the app actually talks to.
Gap assessment, control implementation and evidence preparation for ISO 27001, SOC 2, PCI DSS and India's DPDP Act, through to audit support.
Runbook development, tabletop rehearsal, and hands-on containment, forensics and recovery support if something has already happened.
Testing blind is realistic but shallow; testing with full access is thorough but not what an attacker faces. Neither is correct in general — the right depth depends on what you are trying to learn.
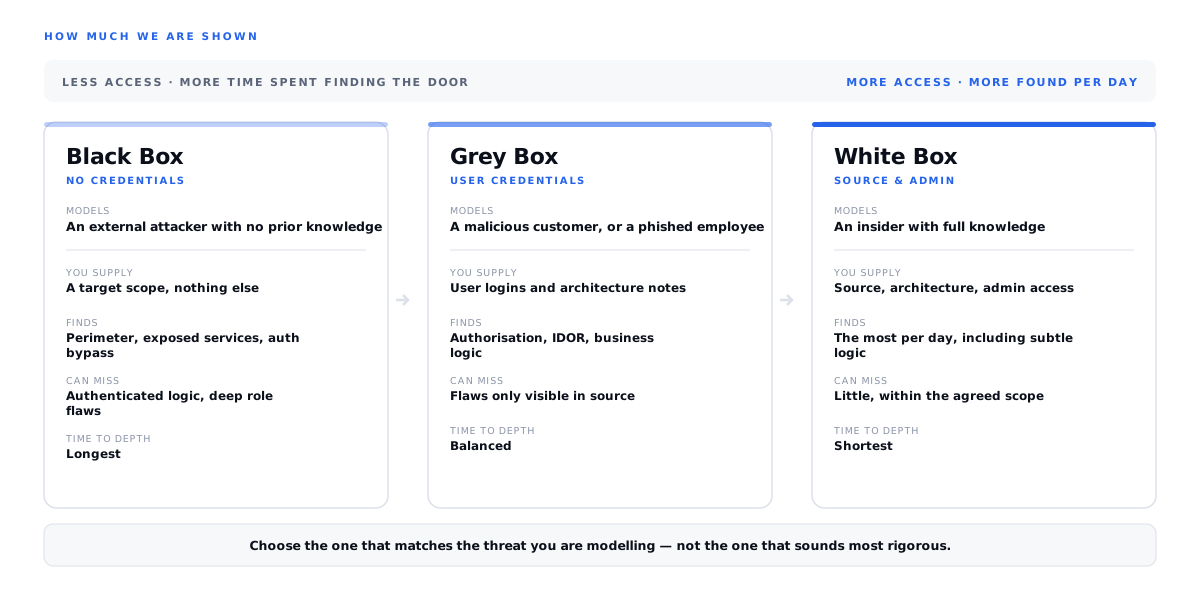
Choose to simulate an outside attacker
We start with what anyone on the internet can see. Closest to a real opportunistic attack, but limited — anything behind a login is largely out of reach in the time available.
Choose for the best coverage per rupee
We are given user-level accounts across roles. Time goes into finding privilege escalation, broken access control and logic flaws instead of into the reconnaissance phase.
Choose before an enterprise security review
Full access to source, architecture and admin. The deepest coverage available, and the right choice when a customer's security team is about to ask hard questions.
Whether you are closing an enterprise deal, entering a regulated sector or operating under Indian data law, these are the standards that come up. We work to all of them.
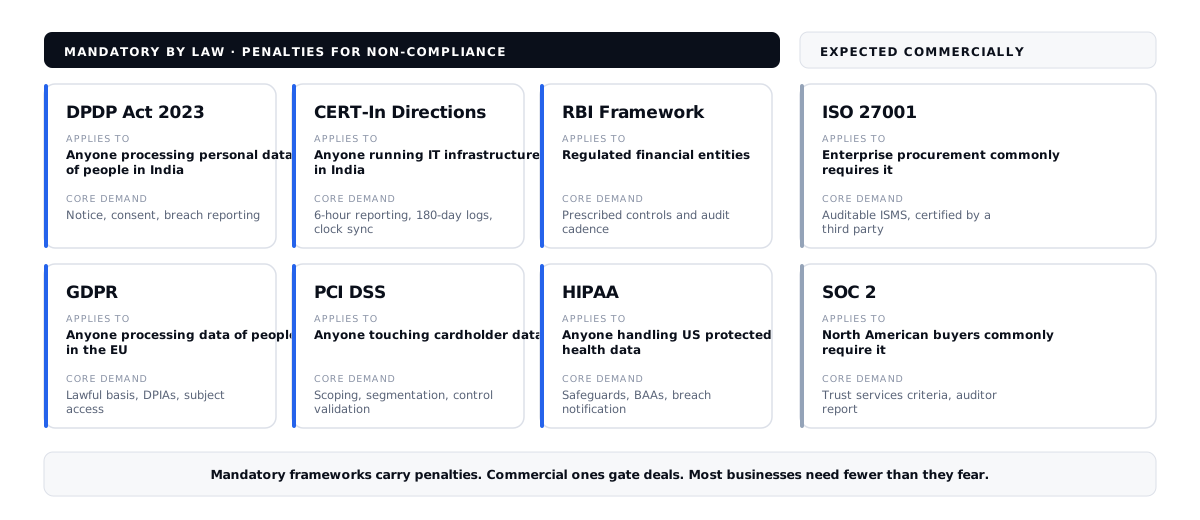
ISMS scoping, controls, internal audit and certification support.
Trust services criteria, evidence collection and auditor readiness.
Consent, notice, data principal rights and breach reporting.
Lawful basis, DPIAs, subject access and cross-border transfers.
Cardholder data scoping, segmentation and control validation.
Log retention, clock sync and six-hour incident reporting.
Cyber security expectations for regulated financial entities.
Safeguards for health data in products serving US healthcare.
Compliance is an outcome of controls, not a substitute for them. We implement and evidence the controls first, and the certificate follows because the underlying work is real — which is also what survives the audit after the one that awarded it.
These fifteen items are not line-items on a quote. They apply to every engagement, at every scope, because a security assessment missing any one of them produces a document rather than a safer system.
Automation covers breadth and known signatures efficiently. Everything that actually matters — access control, business logic, chained exploits — is found by a person who understood the system first.
Nothing is touched before the rules of engagement are signed, and nothing is closed before it is retested. Each stage closes with a named deliverable you review.
Targets, testing windows, escalation contacts and explicit out-of-scope systems are agreed and signed. Nothing is touched until authorisation is documented on both sides.
Deliverables
Attack surface mapped, technologies fingerprinted, and automated discovery run across the agreed scope to establish the baseline before manual work begins.
Deliverables
The part scanners cannot do: access control, authentication, business logic and chained exploits, each verified by reproduction rather than reported on a signature match.
Deliverables
A report written for two audiences — an executive summary of risk, and developer-facing detail with the specific change required — plus a working session with your engineers.
Deliverables
Once fixes are deployed we retest every finding and regression-check the surfaces around them, then issue a closure report stating what is resolved and what residual risk remains.
Deliverables
Most clients start with a point-in-time assessment, often because a customer contract requires one. What it finds usually decides whether the next step is a retainer or a compliance programme.
A test before launch or a customer review
A scoped penetration test with full reporting, remediation support and a retest, delivered for a fixed price. The usual starting point and often what a client contract requires.
A product shipping every week
Recurring testing aligned to your release cycle, dependency and cloud posture monitoring, and a standing channel for security questions as features are designed.
A certification with a deadline
Gap assessment through control implementation, evidence collection and auditor liaison for ISO 27001, SOC 2 or DPDP readiness, run to your certification date.
Every engagement is quoted against a written scope and rules of engagement, so the number you approve is the number you pay.
The questions teams actually ask before commissioning security work, including what to do if something has already happened.
Cost tracks scope and depth rather than a per-asset rate. A single web application tested grey box sits in a very different bracket to a full infrastructure, cloud and mobile assessment run white box with a compliance deliverable attached. We quote a fixed figure against a written scope, and the retest is included rather than billed as a second engagement.
A scan is automated pattern matching: fast, cheap, and useful for catching known issues and missing patches. A penetration test is a person attempting to actually exploit what they find, chain it with other weaknesses and reach something that matters. Scanners cannot find broken access control, business logic flaws or privilege escalation paths, which is where the serious findings usually are. Be wary of any quote where the deliverable is a scanner export with a cover page.
About six weeks for a full cycle. That is one week of scoping and authorisation, one week of reconnaissance, and two weeks of manual testing. Reporting and remediation support take a week, with a final week to retest once your fixes are deployed. The testing window itself varies with depth — black box is typically one to two weeks, white box three to four.
Not without your explicit agreement. Testing windows, rate limits and out-of-scope systems are agreed in the rules of engagement before anything starts, and anything genuinely destructive is either excluded or run against a staging replica. We keep an escalation contact live throughout, so if something behaves unexpectedly, testing stops immediately.
We help fix them. The report includes developer-facing guidance describing the specific change needed, not a generic description of the vulnerability class. We also run a working session with your engineers to walk through the findings. Where you would rather we implement the fixes ourselves, we can — and every finding is retested before the engagement closes either way.
Yes. We run a gap assessment against the standard, implement the missing controls with your team, and establish the evidence trail those controls generate. We then prepare you for the external auditor, who must be an independent certification body rather than us. Most clients on a normal starting position need somewhere between three and six months, driven mainly by how much evidence history the auditor expects to see.
The Digital Personal Data Protection Act 2023 sets five main obligations. You need clear notice and consent for personal data processing, and you must honour data principal rights including correction and erasure. You also need named responsible contacts, reasonable security safeguards, and breach reporting to both the Data Protection Board and the affected individuals. In practice it means knowing what personal data you hold and where, which is where most organisations discover the real gap. We map that, then build the consent, rights-handling and breach processes around it.
Contact us and we will help with containment first: isolating affected systems and preserving logs before they rotate away. The next job is establishing what was actually accessed rather than what was feared. From there we support forensic analysis, recovery, regulatory notification within the applicable windows including CERT-In's six-hour requirement, and the post-incident work to close the path that was used.
You can check before you call us. Run asematic.com through any public header scanner and you will find HSTS with a two-year max-age, includeSubDomains and preload; a Content-Security-Policy denying framing; X-Frame-Options set to DENY; nosniff; a strict referrer policy; and a Permissions-Policy switching off camera, microphone, geolocation and interest-cohort. It is a small thing to check and a fair proxy for whether a security supplier practises what it sells.
Testing at the end finds what was built in at the start. These are the pieces where those decisions are actually made.
Send us the application, the customer security questionnaire you are stuck on, or the certification deadline you are working toward. You will get a scoped plan and an honest read on the effort — before any commitment.